About Us
MedOS HK is the healthcare system integration and information security unit serving hospitals, clinics, insurers and healthcare groups in Hong Kong. Leveraging deep domain knowledge in clinical and insurance systems, MedOS HK provides end-to-end eHRSS connectivity, private Third Party Administrator (TPA) platforms, insurance EDI integration, clinical interface development, and compliance programmes aligned with ISO 27001, SOC 2, HIPAA and GDPR.
Why Engage MedOS HK
Healthcare specialists. We focus exclusively on clinical workflows. Our team understands CMS, LIS, RIS/PACS and the operational realities of Hong Kong healthcare providers — so integrations fit the way your clinic actually works.
eHRSS ready. We connect Clinical Management Systems to Hong Kong's Electronic Health Record Sharing System for record upload and viewing — including patient identity matching, sharing-consent handling and sharable-data mapping.
Private TPA & insurance EDI. We build and operate private Third Party Administrator systems for insurers and scheme administrators, and integrate Electronic Data Interchange (EDI) for eligibility, pre-authorisation, claims submission and remittance — between clinics, TPAs and insurance platforms.
Security by design. Encryption, access control and audit logging are built into every interface from day one, not bolted on after go-live. Threat modelling and penetration testing are part of our standard delivery.
Audit-ready evidence. Operating evidence for ISO 27001, SOC 2, HIPAA, GDPR and the Hong Kong PDPO is produced as you run — so compliance reviews do not become a separate project.
Local support. Our team is based in Hong Kong. Enquiries are handled in English, Cantonese and Mandarin. We reply within one business day.
One partner for integration and security. Most healthcare IT projects split these across vendors. MedOS HK delivers both under one roof, reducing hand-offs and accountability gaps.
Our Services
| eHRSS Integration Connect your CMS to eHRSS for record upload and viewing — identity matching, consent and data mapping. |
Clinical Systems Integration HL7 v2, FHIR and custom interfaces between CMS, LIS, RIS/PACS, pharmacy and billing. |
| Healthcare Cybersecurity Threat modelling, penetration testing, architecture review and hardening for clinical networks. |
Compliance & Audit Readiness Gap assessments, ISMS build-out and evidence automation for ISO 27001, SOC 2, HIPAA, GDPR and PDPO. |
| Private TPA System Design, build and host private Third Party Administrator platforms — membership, eligibility, pre-auth, claims adjudication and provider networks. |
Insurance EDI Integration Electronic Data Interchange between CMS, TPA and insurers — eligibility checks, pre-authorisation, claims submission, status and remittance advice. |
| Managed Security & Monitoring 24/7 log monitoring, vulnerability management and incident response playbooks for healthcare. |
Secure Infrastructure Private and hybrid hosting with encryption, key management, backup and data-residency controls. |
Project Reference — eHRSS & CMS Integration
Client: Private healthcare provider, Hong Kong
Scope: System integration, information security, compliance
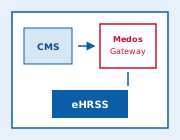
The provider needed its CMS to share clinical records with eHRSS and let clinicians view patients' shared records at the point of care, without exposing sensitive data or disrupting clinic workflows.
Work performed:
- Integration layer between the CMS and eHRSS interfaces
- Patient identity matching and registration status checks
- Sharing-consent verification before any record access
- Mapping of CMS data to eHRSS sharable data domains
- Encryption in transit and at rest; role-based access
- Tamper-evident audit trail; conformance testing and go-live support
| Phase | Activities |
|---|---|
| 1. Discovery | Data flow mapping, privacy impact, threat model |
| 2. Architecture | Gateway design, key management, network segmentation |
| 3. Build | Interface development and clinical data mapping |
| 4. Verification | Conformance testing, penetration testing, clinician UAT |
| 5. Operation | Monitoring, audit evidence and continuing support |
Outcome: Clinicians see a patient's shared history inside their existing CMS, records flow to eHRSS automatically, and every access is logged and reviewable — with audit evidence ready for ISO 27001 and SOC 2.
Compliance & Standards
| Framework | Scope | How we address it |
|---|---|---|
| ISO/IEC 27001 | Information security management | Risk treatment, access control, supplier security |
| SOC 2 | Trust Services Criteria | Security, availability, confidentiality, privacy evidence |
| HIPAA | US protected health information | Privacy and Security Rule safeguards |
| GDPR | EU personal data | Lawful processing, rights, breach notification |
| HK PDPO | Hong Kong personal data | Six Data Protection Principles |
Our Approach
- Assess — clinical workflows, data flows and regulatory scope
- Design — threat modelling and privacy by design
- Build — secure SDLC with automated testing
- Assure — penetration test, conformance test, audit evidence
- Operate — monitor, patch, respond and improve
Contact Us
Planning an eHRSS, private TPA, insurance EDI or clinical integration project? Tell us about your systems and compliance goals. We reply within one business day.